Amazon for Organs
Scientists have made major strides towards storing and revitalizing organs for transplants. One step closer to rush delivery of a premium kidney.
I explained the meaning of a "half A-press," but Stuff still Happened.
So, what's up?
Stashin' Organs
We done froze a pig kidney and brought it back. Dang, well done, us.
Well, some of us.
A team of scientists at the University of Minnesota successfully restored a frozen pig kidney to (mostly) working order after having stashed it in the way back of the freezer for over a year. Like, all the way in the back where there's some ice buildup and that decade-old bag of frozen peas that you use sometimes as an ice pack but will never actually use in a recipe out of a sense of self-preservation.
Er,
So, pig kidney. Cryopreservation. That stuff. Okay—so, they froze the kidney down to -150℃, preserving them in some cases for over a year. They then used some wild tech to thaw it back out to be tested in action. Some kidneys were tested using a machine that supplies organs with nutrients, while others were transplanted into actual pigs. They were happy to report that the kidneys regained color and began producing urine, which shows at least a partial success.
Can't say for sure if they'll continue working, or how well, but they did a non-zero amount of "coming back to life."
When I say "wild tech" to thaw out the organ, I mean it. It's a difficult problem to solve: how do you evenly thaw out something as delicate as an internal organ without either dealing with ice crystal formation or hurting the tissue?
The answer is obvious: nanoparticles and electromagnetic radiofrequencies. Fucking duh, bro.
In addition to filling the organ with a solution to prevent icing, they seeded the organ with nanoparticles of iron oxide, which is inert until hit with an electromagnetic field to heat up and manage the thawing process throughout the organ.
Simply harvest an organ, imbue it with nanoparticles, and manipulate electromagnetic fields, and you're all set to start your own organ warehouse.
Maybe—actually—uh, don't do that.
So our future may eventually feature some kind of organ warehouse where you can choose a boutique spleen or whatever. Like an Amazon for organs. Though, to be clear, that's a decent way off. This is still an early step towards such a world, though not the first one! We've previously seen similar success in rat and mouse organs, though of course those are far, far smaller than a pig's.
If the timing works out, I'll see about having my organs preserved in case anyone wants to bid on my gallbladder.
Yemen War Resurgence
The civil (and proxy) war in Yemen is raging at full force again, ramping up from a period of relatively reduced action since 2022.
Let's start with the basics: what is going on in Yemen, who are the players, and why?
The current civil war in Yemen began in full force in 2014 when Houthi forces launched an assault on Sanaa, the capital of Yemen. The Houthis (aka Ansar Allah) are a political and paramilitary organization that rose to prominence over the 1990s, early 2000s and into the Yemeni Revolution in 2011.
The globally recognized Yemeni government is led by the Presidential Leadership Council (PLC). The Houthis oversee a separate, unrecognized government entity called the Supreme Political Council (SPC). Trust me when I say I keep mixing up these terms, too.
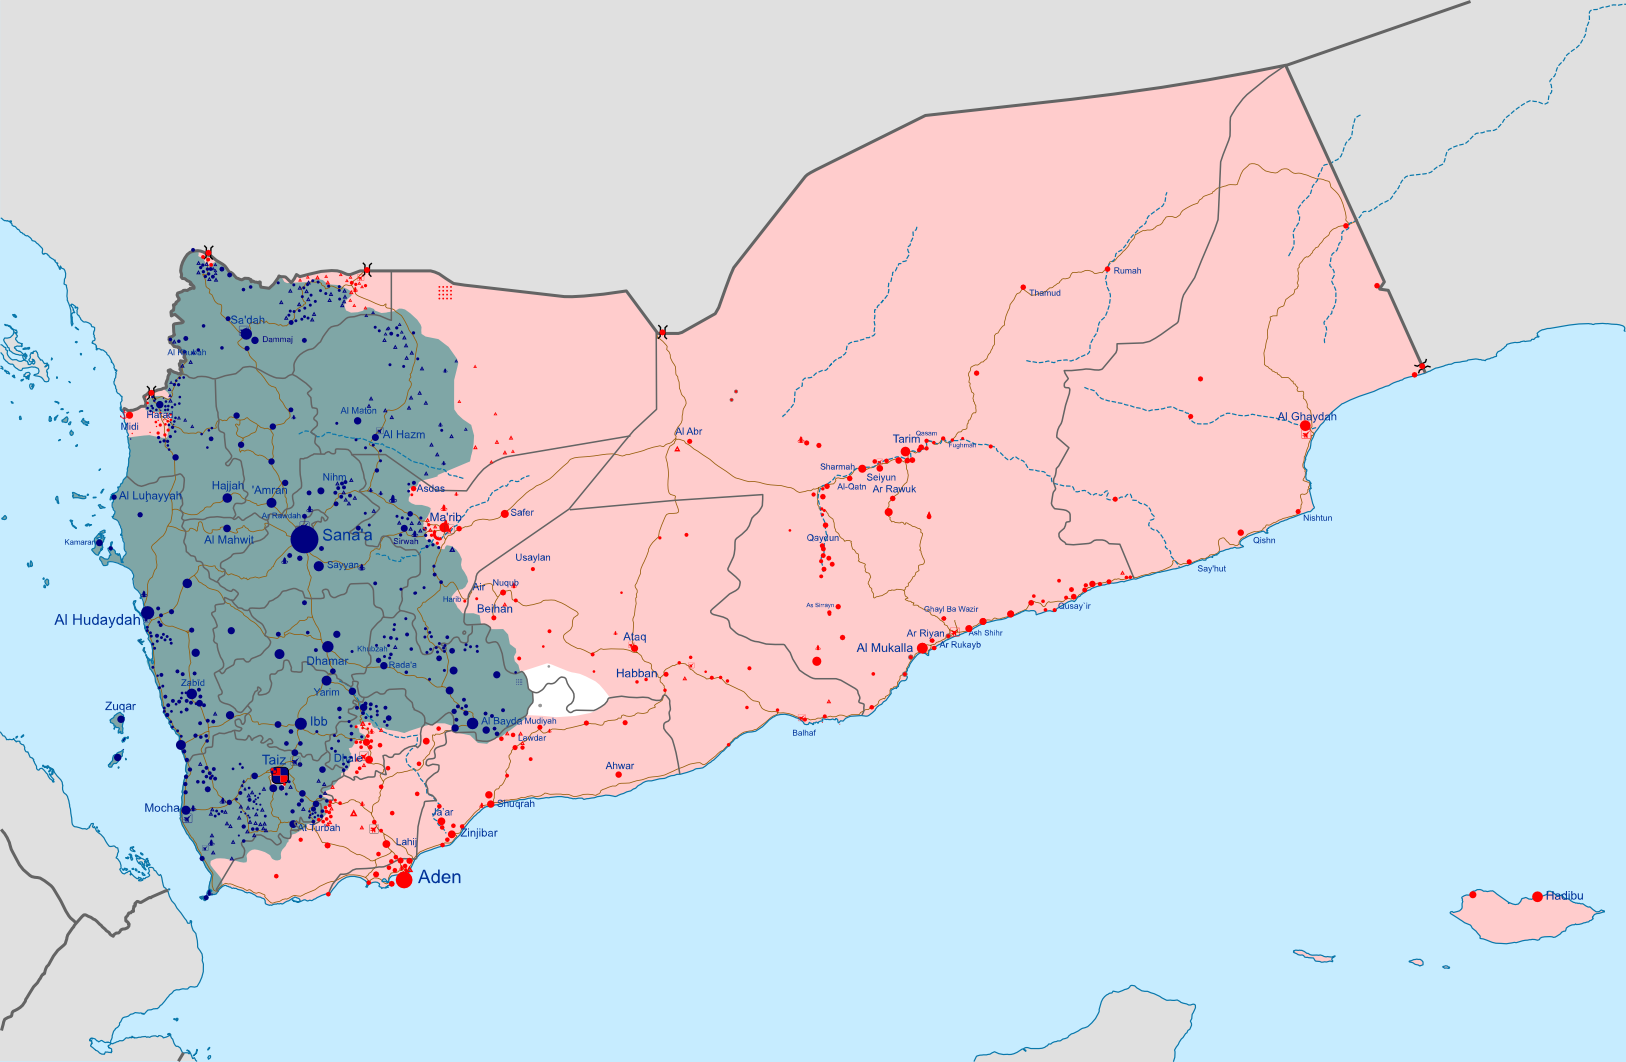
The Houthis control a populous chunk of Yemen's western edge, with the remainder of the country fractured between various factions.
At this point, it's important to note that this doesn't end at the borders of Yemen. The Houthis and the recognized government both have their own third-party backers, and those third parties don't all agree on what the outcome should be, even when backing the same "side."
Saudi Arabia and the United Arab Emirates are both aligned against the Houthis, though they have differing end goals for the state of Yemen. Meanwhile, Iran backs the Houthis, supporting them as a part of their "Axis of Resistance" to expand regional influence.
With a recent resurgence in fighting after the United States and Israel began their war on Iran, Saudi Arabia and the UAE are now trying to figure out if they can reconcile their disagreements in order to unify against Iran's influence in the region.
All the while, the humanitarian toll is tremendous. Hundreds of thousands of people have died in this war, and several million more are currently displaced, many without access to clean water or food.
It's a mess. It is a civil war with significant internal and external stakes, as well as another front in a proxy war between major powers in the region.
My heart is with the people of Yemen.
The United States Goes after Kyle
An interesting federal court case cropped up out of Oklahoma, where a traffic stop resulting in a drug bust may have wide implications for Flock cameras. Maybe.
The case is the United States v. Kyle (dang, Kyle, that's heavy). The case itself is fairly simple: woman charged with transporting a lot of drugs in her car after being pulled over for a traffic stop.
What makes this interesting is what happened leading up to the driver's encounter with the officer, and how the court has responded.
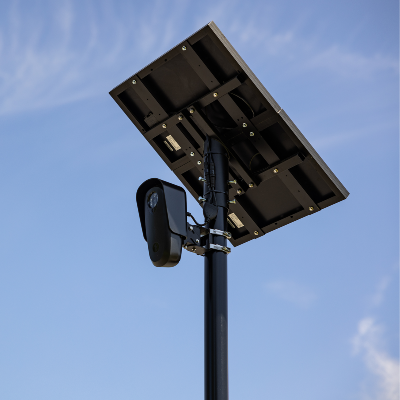
Melisa Susan Kyle, the defendant in the case, filed a motion to suppress evidence acquired by police in part using Automated License Plate Reader (ALPR) technology, claiming that it constituted unreasonable search and seizure. When she was originally pulled over, the officer had already run her plates through two surveillance camera networks to see where she had been. They returned more than 50 results from the prior 30 days.
The court found that the officer's only reasoning for performing his search was that her car had a California license plate. Eventually, he pulled her over for such traffic violations as "not signaling before changing lanes" and "following a car too closely," which—I mean, if that's enough to get pulled over, then every single person on the road where I live should be in jail.
The officer questioned Kyle for a bit, and while her story was a bit odd, nothing she said stood out as an outright "gotcha" moment. For example, she had a lot of luggage in her car for one person, which she explained was because she bought a lot of clothes and so also bought more luggage while she was on a trip to California to see family. Her story was a bit strange, but the court didn't find that to be probable cause for a search.
The officer also ended up handing Kyle back her ID, which legally should have ended the stop. Instead, he asked her more questions, detained her, and called out a drug sniffing dog.
Per the court…
The Court agrees that the amount of luggage Kyle had in her vehicle was a little excessive. But the problem for the government is that excessive luggage, while odd, does not necessarily establish reasonable suspicion.
Pretty chill of the court, honestly. But actually, they get chiller. See, the officer used ALPRs to pull up information about this person's travel history based on essentially nothing. When officers access that data, they must provide a reason for doing so. The officer's reasons were "investigation" and "traffic violation," which aren't particularly excellent supporting arguments for why you've accessed a national location database.
The court found that the wide scale fetching of this data without a warrant violates the Fourth Amendment of the United States Constitution which protects from unreasonable search and seizure. Still, the court ruling makes it clear that ALPRs in abstract do not break the Fourth Amendment inherently, but does go on to call out that the legal basis for courts allowing the continued use of ALPRs is questionable.
For example, one of the primarily cited cases when dealing with these systems is United States v. Knotts, which established that there is not a reasonable expectation of privacy for drivers on public roadways. Seems open and shut! Except, quoting that court case…
[…] if such dragnet type law enforcement practices as respondent envisions should eventually occur, there will be time enough then to determine whether different constitutional principles may be applicable.
It was over 40 years ago that the SCOTUS wrote those words. I think the establishing of a national network of location tracking systems which record the whereabouts of all individuals indiscriminately is uh, probably constituting "such dragnet-type law enforcement."
Anyway, don't smuggle drugs. And if you do, don't get caught. And if you do, don't answer questions. Never talk to the cops without a lawyer present. Ever. Even if they're "just asking questions." Remember: cops are legally allowed to lie to you to set you up for self incrimination.
As for Kyle's case, the prosecutors are now unable to use the ALPR location history, and uh, they also can't use the dozens of pounds of drugs they found as evidence, since they were discovered after the traffic stop should have legally ended.
I'd expect an appeal, but as it stands, the case basically just blew up in the government's face.
The Number 4
Hey—if you participate in securing the internet via cryptography services, maybe be sure that your cryptography services are, like, secure.
You may have seen some generally IT-aligned people running around the past few days like chickens relieved of their heads. Luckily for you, dear reader, it's likely that you are mostly fine from any impacts of the situation that these poor, poor IT folks are currently navigating. That is, unless you're an IT folk. In which case, ope.
THE INTERNET. It is a bunch of devices making a bunch of connections to each other.
To make connections secure, devices rely on "keys" and "certificates" to verify the connection's authenticity as well as encrypt the data. Certificates can be "signed" by a "certificate authority," which is basically an organization who can vouch for specific keys belonging to specific websites.
If someone got ahold of a certificate authority's secret digital keys, they could impersonate the authority and thus create their own certificates. That could potentially allow an attacker to impersonate a website if the device making the connection hasn't been updated with a fix.
Devices—such as the one you're using to read this right now—have an internal database of approved certificate authorities and related cryptographic information. All of this happens automatically for every secure connection your device makes.
So here is the shot: eight keys managed by Indian certificate authority eMudhra were compromised. Turns out the keys were just so incredibly insecure that they could be guessed. One of them was literally the number "4".
The type of key in question is a P-384 elliptic-curve key. A correctly generated key uses a secret number that can be around 116 digits in length. One of the compromised keys in question was instead 4.
THAT'S NOT SUPPOSED TO HAPPEN. The company said it was the result of a flaw in their key generation which created a set of weak keys which were accidentally approved for use. That... that doesn't really explain things sufficiently for me, at least.
But don't panic. Major web browsers and operating system providers have already pushed emergency updates to prevent the use of these broken keys. It is unlikely that you will run into any issues while surfing the information superhighway. Maybe make sure your browser and device is up-to-date though.
The real danger lies in embedded systems, obscure server software, and old software that will need to be found, patched, and re-deployed. It'll take quite some time to find and fix all of the software and systems that still errantly trust the busted keys.
There is currently no evidence that the Bad Keys were used to make more keys by the time the vulnerability was discovered, so that's a good start.
My advice: don't use the number 4 as a private key.
Here's the Weather
More Stuff
- The next season of True Detective will co-star Nicolas Cage and Antonio Banderas, which may ultimately result in the total annihilation of television as we know it
- A woman from El Salvador threw herself overboard off of a cruise ship and was found almost a day later floating in the water by Greek authorities
- Two gas stations in Georgia got into a pricing war and ended up selling gas for less than a dollar, sparking a rush big enough to draw police to get involved
- An Xbox business strategy manager took to Twitter to rant about how people need to accept AI in gaming, then deleted his account after throwing a fit when people pushed back
- A preliminary study showed that microdosing LSD resulted in better focus for women but no change for men
- Elon Musk now wants to merge SpaceX and Tesla after merging SpaceX, Twitter, and his AI company
- A bunch of Republicans and Business Boys are mad at the CEO of United Airlines for supporting the idea of a national wealth tax
- Note: this does not absolve the CEO of United Airlines of the crime of being the CEO of United Airlines